grawk
Administrators
-
Joined
-
Last visited
Everything posted by grawk
-
Lots of people in team source dead fucking last
-
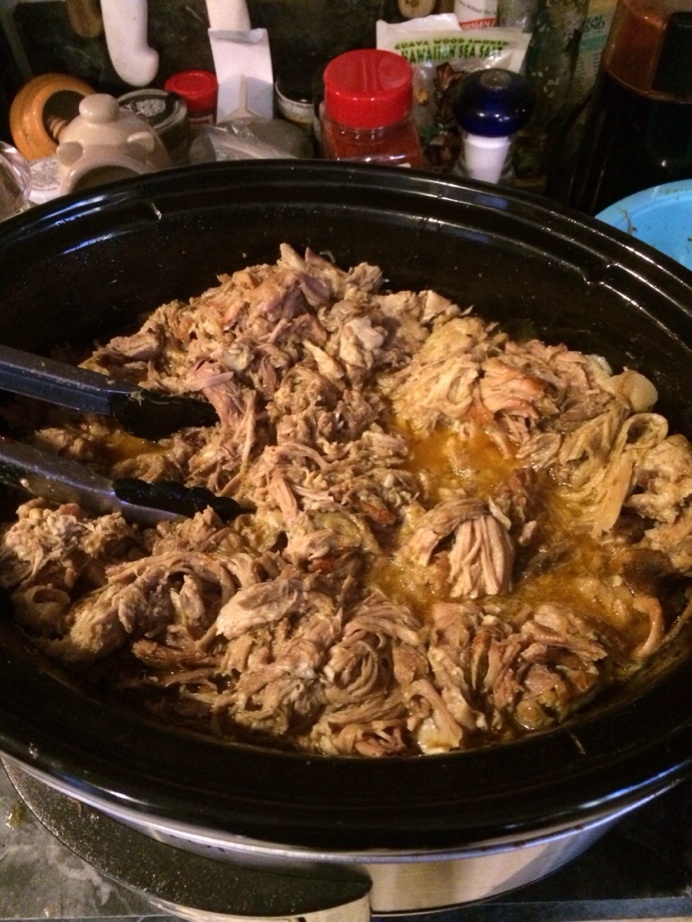
Pulled pork

-
-
the show had garnered pretty universal acclaim starting back with season 2, everything that showed up at the end was in the show from the beginning...I'm pretty sure the writers knew where they were going from the start.
-
how is that mehliana, Al? I'm listening to De La Soul
-
hint: any developer can do malicious things via updates. Don't install stupid shit.
-
I"m listening to this one now
-
The Sweep - Starlight City Moans (feedbands 7) digital download
-
also doesn't help that I'm reading a paranoid techno thriller and have insomnia
-
I'd say don't freak out. at this point it'll blow over and just be a headache for the people it impacts. it's more people on my side of the computer that will have the real issues to deal with. and the insurance companies, maybe. it's kinda like the target thing.
-
the insidious thing about the openssl problem is that the man in the middle attack could be coming from ANYWHERE in the middle. The more I think about it the more I want to go back to face to face banking. The scope of this could end up being bigger than the backdoor that was in the openssl libraries for over 10 years.
-
This is a privacy/security problem (that may be more widespread than is currently being reported). There is a separate ball of wax that is the windows malware situation.
-
it isn't. That's what I'm recommending. Don't use your computer on any public network.
-
this exploit puts "the adversary" in the middle of your encrypted connections (and anyone else's) if they've taken control of the network. Network sniffing is a different problem. Both are solved with a mifi.
-
if the students are on the network you use, I'd to the opposite, and VPN home
-
It's probably never a bad idea to change important passwords, and enable 2 factor authentication whenever you can. Do it from home or work tho... Also, 15 character passwords, mixed for anything that matters. There are lookup tables for almost anything less than that readily available in the black hat world.
-
cool My job has me so paranoid about network activity in general...
-
Does UC have separate real and student networks? Because I know at the university of alaska, the student network was a cesspit.
-
it's the "afaik" that's important. You don't know. You have no way of knowing. I personally won't use a mac except on my home network at this point. Tho in all likelihood, the damage has been done, if it's going to be. That said, I'm not particularly worried about personal consequences so much as potential work consequences. I stopped using my work computer on non-work/home/mifi networks 2 years ago tho, and all traffic is vpn on it.
-
I think it's fair to say everyone's being targeted if you get on a network that's been hacked. As to what you have to lose, well, it depends on what you use your computer for. This one isn't minor.
-
unless sprint's network's been exploited you should be fine
-
maybe?
-
it's only bad if you use your mac for work, financial transactions, shopping, or email. Oh, or calendaring.
-
yes more specifically: immediately upgrade your iphone, and stop using safari on your mac.
-
Thanks Matt, you too!